The outcome is only the beginning.
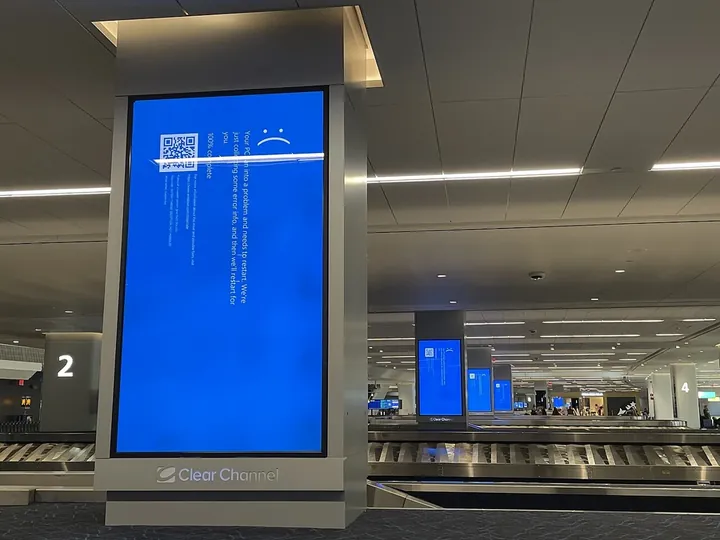
A Channel File 291 update triggered Windows crashes on affected systems. [1]
Treat rapidly delivered security content as production code; stage it, validate interface contracts, and test offline recovery.
What the system was trying to do.
Update endpoint protection against emerging threats.
The assumption beneath the promise
Museum hypothesis to examine: Validation of one representation proves that the downstream consumer will interpret it safely. This is an analytical proposition to test against the record, not an attributed statement by the organization.
Success should be assessed against the intended service and its safety, reliability, or integrity constraints. A headline outcome cannot tell us whether those constraints were visible, tested, or owned before the event.
A sequence, not a single moment.
The intended system
Update endpoint protection against emerging threats.
Source-backed synopsisThe event or review
A Channel File 291 update triggered Windows crashes on affected systems. [1]
Source-backed synopsisThe documented aftermath
CrowdStrike published an RCA and described testing and deployment changes. [1]
Source-backed synopsisWhat could be seen at the time?
The root-cause analysis examined a mismatch in content expectations and validation. [1]
Who could see it?
See the cited investigation for named teams and the information they held. The synopsis does not infer awareness by every stakeholder.
Why was it not enough?
Signals need interpretation, authority, and a route to action. This is an analytical question, not proof that a warning was deliberately ignored.
Choices made within constraints.
Museum analysis: Security-content delivery needed safeguards appropriate to its privileged execution environment.
Available alternatives
Pause, test, narrow the operating envelope, seek independent review, or build a recovery option. These are proposed analytical alternatives; feasibility at the time is not established.
Information available
The root-cause analysis examined a mismatch in content expectations and validation. [1]
Incentives & constraints
Delivery pressure, cost, authority, and incomplete knowledge may shape a decision. Their specific weight is not established by this synopsis.
Risk accepted
Ask whether the relevant risk was recognized, who had authority to accept it, and whether affected people understood its implications.
How conditions connected.
Select a node to inspect its evidence. Links show a proposed analytical relationship, not a measured causal effect.
A Channel File 291 update triggered Windows crashes on affected systems. [1]
Beyond the immediate event.
Organizations across many sectors had to restore affected endpoints. [1]
Categories identify documented or relevant consequences. Financial, human, and environmental totals are not estimated here when the source base does not support them.
More than one lens.
Swiss Cheese Model
Harm can pass through gaps in multiple defenses: organizational influences, supervision, preconditions, and active failures.
In this case, use the lens to examine validation gap. This application is museum interpretation, not a finding of the original investigation.
Limit: A useful lens, not proof of a universal linear cause. Barriers interact and change over time.
FMEA
Identify failure modes, their effects, and controls before or during system development.
In this case, use the lens to examine validation gap. This application is museum interpretation, not a finding of the original investigation.
Limit: Lists can miss interactions and unanticipated operating conditions; scores are not exact probabilities.
Root Cause Analysis
Use structured evidence to identify contributory conditions and corrective actions.
In this case, use the lens to examine validation gap. This application is museum interpretation, not a finding of the original investigation.
Limit: Introductory guide. This lens generates questions; it does not establish causation or replace case-specific evidence.
What could have changed the outcome?
Counterfactuals are hypotheses. They identify possible intervention points without claiming that a different choice would certainly have prevented the event.
Test the operating envelope
Exercise realistic boundary conditions and shared dependencies rather than validating components only in isolation.
Cost & feasibility
Requires time and independent review before commitment.
Likely effectiveness
May reduce exposure or consequences. Not quantified; feasibility and effect must be assessed against evidence available at the time.
From hindsight to a usable practice.
Treat rapidly delivered security content as production code; stage it, validate interface contracts, and test offline recovery.
Before accelerating hiring or spending, name the assumptions that remain untested and set evidence thresholds for the next commitment.
Recovery is another investigation.
CrowdStrike published an RCA and described testing and deployment changes. [1]
A corrective action is evidence of a response; it is not, by itself, evidence that the wider pattern has disappeared.
Follow the record.
Documented claims are linked to sources. Analytical applications, lessons, and intervention proposals are museum interpretation. This draft does not establish motives or a single complete causal explanation.
- 1crowdstrike.com — CrowdStrike case record
Technical postmortem · Accessed 4 October 2026
Editorial history & limits
Version 1 · 4 October 2026 — source-backed illustrative synopsis created. Independent editorial review is pending. No claim of exhaustive investigation. New sources may alter the analysis.